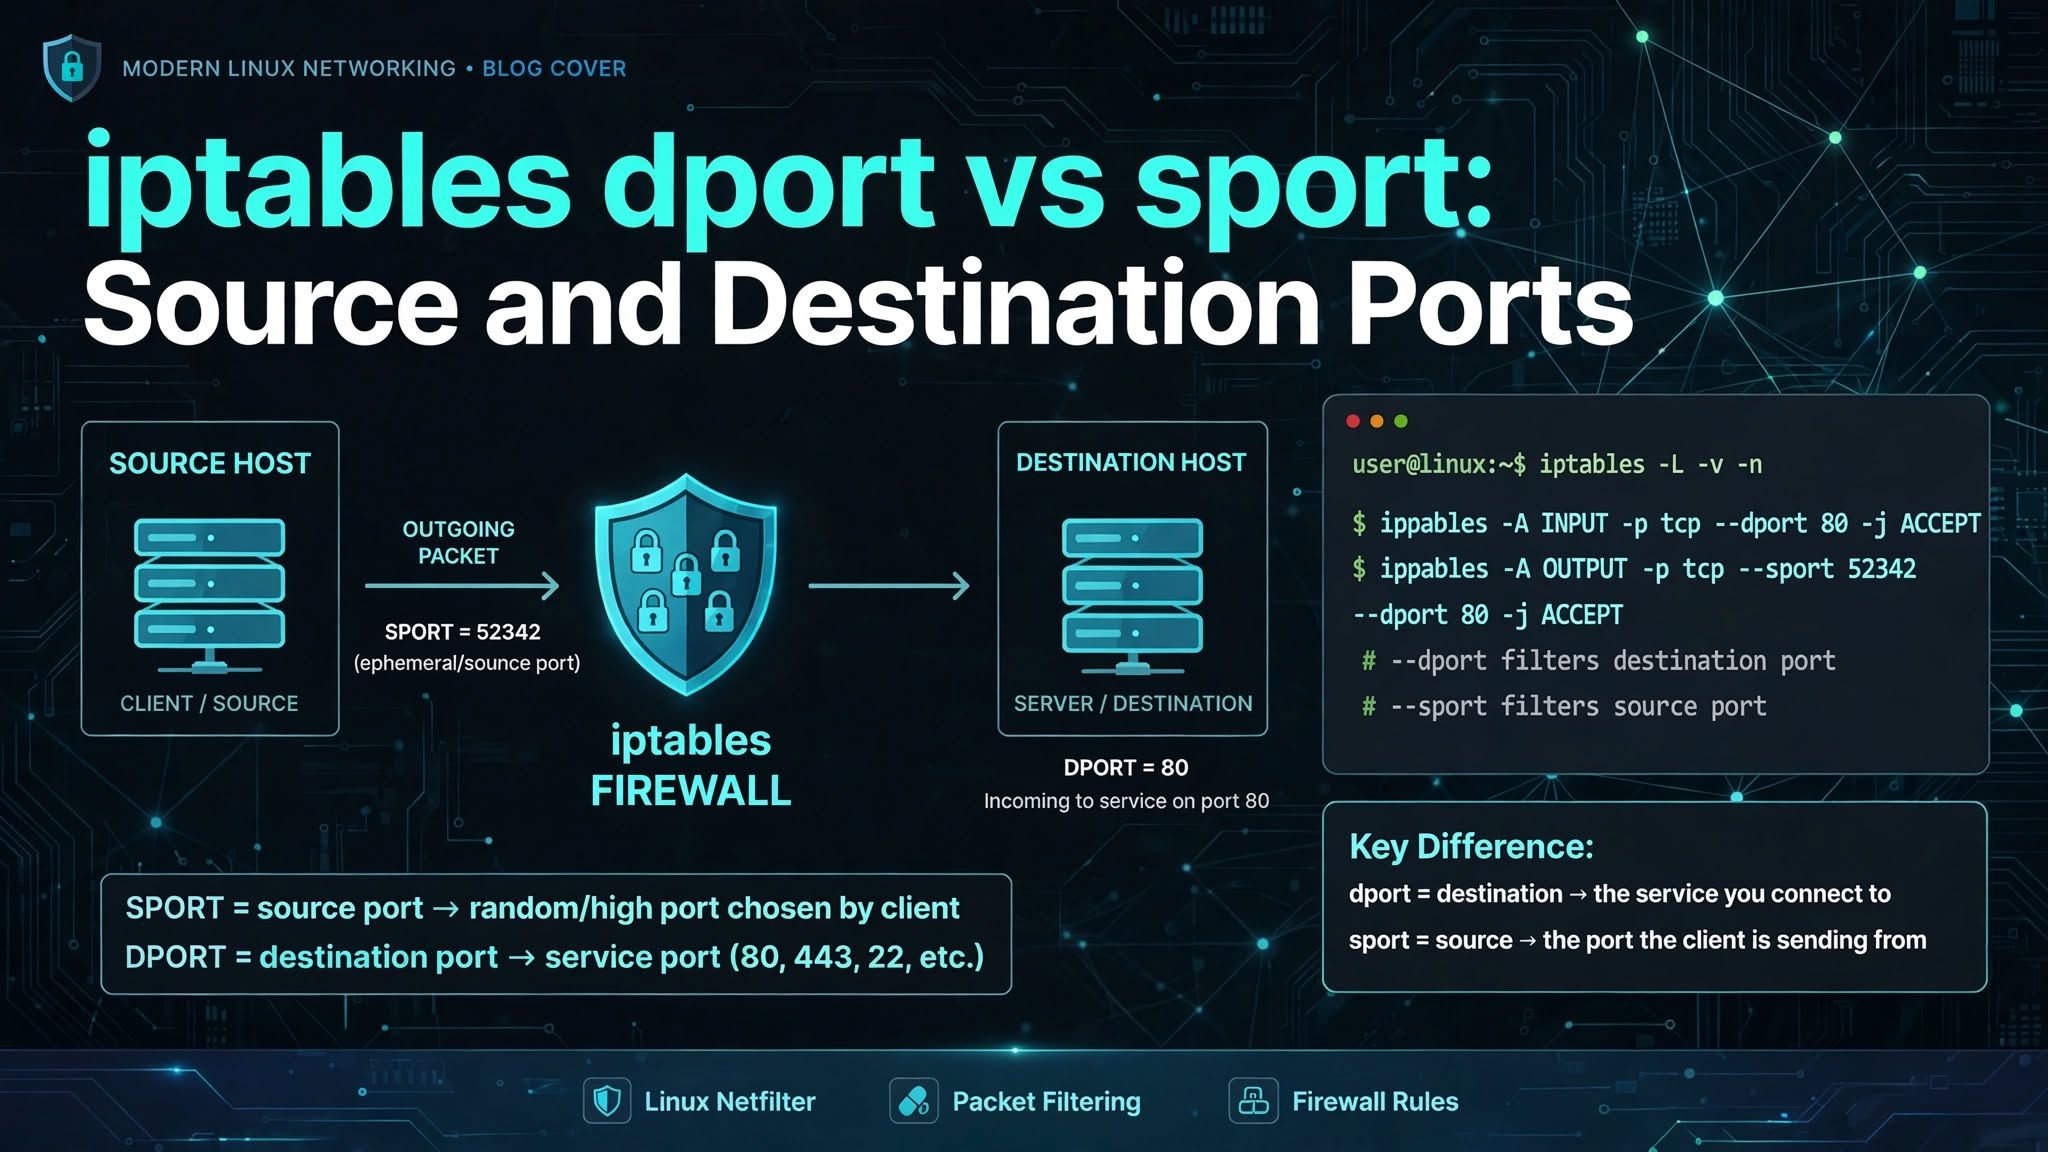
On Ubuntu or Debian, install iptables-persistent, save the current IPv4 rules to /etc/iptables/rules.v4, and verify that netfilter-persistent is enabled. RHEL-family systems use their distribution firewall service or a systemd restore unit.
Why Save iptables Rules?
iptables is like a security guard for your Linux system. It controls incoming and outgoing traffic. But by default, iptables rules disappear after a reboot. This guide shows you how to make them permanent.
3 Easy Ways to Save iptables Rules
1. Manual Method: Save and Restore Rules
This works on all Linux systems (Ubuntu, CentOS, etc.).
Steps:
-
Save your current rules to a file:
sudo iptables-save > /home/user/my_iptables_rules.txt(Replace
/home/user/with your home folder.) -
Restore rules after reboot by adding this line to
/etc/rc.local(a startup script):sudo iptables-restore < /home/user/my_iptables_rules.txt
Example:
- You block a malicious IP (
192.168.1.100) with:sudo iptables -A INPUT -s 192.168.1.100 -j DROP - Save it with:
sudo iptables-save > /home/user/block_malicious_ip.txt
Fix Common Errors:
- “Permission denied”: Use
sudobefore commands. - “Command not found”: Install iptables with
sudo apt install iptables(Ubuntu) orsudo yum install iptables(CentOS).
2. Ubuntu/Debian: Use iptables-persistent
This tool automatically saves and restores rules.
Steps:
-
Install it:
sudo apt update sudo apt install iptables-persistent -
During installation, say “Yes” to save current rules.
-
To save rules later:
sudo netfilter-persistent save
Example:
- You allow SSH (port 22) with:
sudo iptables -A INPUT -p tcp --dport 22 -j ACCEPT - Save it with:
sudo netfilter-persistent save
Where Are Rules Stored?
- IPv4 rules:
/etc/iptables/rules.v4 - IPv6 rules:
/etc/iptables/rules.v6
3. CentOS 7: Use iptables-services
CentOS 7 uses firewalld by default, but you can switch to iptables.
Steps:
-
Stop and disable
firewalld:sudo systemctl stop firewalld sudo systemctl disable firewalld -
Install iptables services:
sudo yum install iptables-services -
Save rules:
sudo service iptables save -
Start iptables on boot:
sudo systemctl enable iptables sudo systemctl start iptables
Example:
- You block ping requests with:
sudo iptables -A INPUT -p icmp --icmp-type echo-request -j DROP - Save it with:
sudo service iptables save
Troubleshooting
Problem 1: Rules Disappear After Reboot
- Fix: Check if you saved rules correctly (e.g.,
sudo netfilter-persistent saveon Ubuntu). - Check: Look for errors in
/var/log/syslogorjournalctl -xe.
Problem 2: “iptables-save Permission Denied”
- Fix: Always use
sudo(e.g.,sudo iptables-save).
Problem 3: Conflict with firewalld (CentOS)
- Fix: Either stick to
firewalldor fully switch to iptables (as shown above).
🔎 People Also Search For
1. Iptables-Save Rules After Reboot
By default, iptables rules reside in volatile kernel memory and are wiped when the machine restarts. To ensure rules persist across reboots:
- Dump existing rules to disk: Use
iptables-saveto write the current active rule set to a persistent file. - Automate reloading on boot: Use systemd services like
netfilter-persistent(Ubuntu/Debian) oriptables.service(CentOS/RHEL) that executeiptables-restorebefore network interfaces come up. - Verify persistence: Run
sudo reboot, log back in, and verify withsudo iptables -L -n -vto ensure custom chains and policies are active.
2. How to Save Iptables Rules Permanently After Reboot CentOS
On CentOS / RHEL (CentOS 7, 8, Stream, AlmaLinux, Rocky Linux):
- Disable firewalld (if using raw iptables instead of firewalld):
sudo systemctl stop firewalld sudo systemctl disable firewalld sudo systemctl mask firewalld - Install
iptables-services:sudo yum install iptables-services -y # or 'dnf' on CentOS 8/9 - Save active rules to
/etc/sysconfig/iptables:sudo service iptables save # Alternatively: sudo iptables-save | sudo tee /etc/sysconfig/iptables - Enable and start the iptables systemd service:
For IPv6 rules, also runsudo systemctl enable iptables sudo systemctl start iptablessudo service ip6tables saveandsudo systemctl enable ip6tables.
3. Save Iptables Rules Ubuntu
On Ubuntu and Debian systems, the standard method uses the iptables-persistent package:
- Install package:
sudo apt update sudo apt install -y iptables-persistent - Save rules anytime after making changes:
sudo netfilter-persistent save - Inspect saved files:
- IPv4:
/etc/iptables/rules.v4 - IPv6:
/etc/iptables/rules.v6
- IPv4:
- Manual one-liner alternative (without prompts):
sudo iptables-save | sudo tee /etc/iptables/rules.v4
sudo ip6tables-save | sudo tee /etc/iptables/rules.v6
4. Iptables-Save Command
The iptables-save utility dumps the current state of IPv4 packet filter tables to standard output (stdout) in a format designed to be parsed directly by iptables-restore.
- Basic command:
sudo iptables-save - Save only a specific table (
filter,nat,mangle,raw):sudo iptables-save -t nat - Include packet and byte counters (
-cflag):sudo iptables-save -c > /path/to/rules.with-counters - Safe write to a privileged file:
sudo iptables-save | sudo tee /etc/iptables/rules.v4
5. Iptables-Persistent Package
iptables-persistent is a Debian/Ubuntu package built around netfilter-persistent. It provides a systemd service (netfilter-persistent.service) that automatically restores firewall rules during system startup:
- Service Status:
sudo systemctl status netfilter-persistent - Save both IPv4 & IPv6 current rules:
sudo netfilter-persistent save - Reload saved rules from disk without rebooting:
sudo netfilter-persistent reload - Flush all active rules:
sudo netfilter-persistent flush
6. Iptables Save Docker
When Docker runs on Linux, it dynamically manages iptables rules (creating DOCKER, DOCKER-ISOLATION, and DOCKER-USER chains) to handle container NAT, port publishing, and inter-container communication.
Common Pitfall: If you run sudo iptables-save > rules.v4 while containers are running and restore that dump on boot, you may lock in ephemeral Docker bridge IPs, causing container networking failures or broken port mappings when the Docker daemon starts.
Best Practices for Docker:
- Use the
DOCKER-USERchain: Put custom firewall rules inDOCKER-USER. Docker guarantees this chain is evaluated before Docker’s default rules and is not wiped when Docker restarts. - Save base system rules before starting Docker, or ensure
netfilter-persistentloads rules beforedocker.servicestarts (using systemdBefore=docker.service). - If managing firewall completely externally: You can disable Docker’s automatic iptables manipulation in
/etc/docker/daemon.jsonwith{"iptables": false}, though you will have to manually configure NAT masquerading and container routing.
7. Iptables-Save Permission Denied
A frequent beginner issue happens when executing:
sudo iptables-save > /etc/iptables/rules.v4
# Error: -bash: /etc/iptables/rules.v4: Permission denied
Why this happens: The sudo command applies only to iptables-save. The output redirection > is handled by your current unprivileged shell session, which cannot write to root-owned directories like /etc/ or /etc/sysconfig/.
How to fix it:
- Method 1 (Recommended - pipe to tee with sudo):
sudo iptables-save | sudo tee /etc/iptables/rules.v4 - Method 2 (Run subshell with sudo):
sudo bash -c "iptables-save > /etc/iptables/rules.v4" - Method 3 (Switch to root temporarily):
sudo -i
iptables-save > /etc/iptables/rules.v4
exit
8. Iptables Save Not Working
If rules still disappear after a reboot, work through this troubleshooting checklist:
- Conflicting Firewall Managers:
- On Ubuntu, check if
ufwis active (sudo ufw status). If active, UFW overwrites iptables on boot. Disable it withsudo ufw disableif you use native iptables. - On CentOS/RHEL, check if
firewalldis active (sudo systemctl status firewalld). Disable and mask it.
- On Ubuntu, check if
- Service Not Enabled in Systemd:
- Verify the restoration unit is enabled:
sudo systemctl is-enabled netfilter-persistent # Ubuntu/Debian sudo systemctl is-enabled iptables # CentOS/RHEL - If disabled, run
sudo systemctl enable netfilter-persistentorsudo systemctl enable iptables.
- Verify the restoration unit is enabled:
- Rule File Location Mismatch:
- Ubuntu expects
/etc/iptables/rules.v4. - CentOS expects
/etc/sysconfig/iptables. Ensure you saved to the distribution’s exact path.
- Ubuntu expects
- Syntax Errors in Rule File:
- Manually test restoration from file to see errors:
sudo iptables-restore -v < /etc/iptables/rules.v4
- Manually test restoration from file to see errors:
- Network Manager / Cloud-Init Resets:
- Certain cloud provider initialization scripts or
NetworkManagerdispatchers flush iptables tables on interface startup. Checkjournalctl -bto see if a networking script resets packet filter tables.
- Certain cloud provider initialization scripts or
Best Practices
- Backup Rules: Save rules before making changes.
sudo iptables-save > /home/user/backup_rules.txt - Test Rules: Apply rules temporarily (
sudo iptables-restore < file.txt) and test before saving. - Add Comments: Use
-m comment --comment "My rule"to explain rules.
Conclusion
Now you know how to save iptables rules permanently on any Linux system! Use:
- Manual method (for all systems),
iptables-persistent(Ubuntu/Debian), oriptables-services(CentOS 7/8/9).
For more help, check:
man iptables(manual page)- Netfilter Docs